Susan Brown joins Mickai as Chief Compliance Officer and Director
Susan will lead Mickai's compliance function, oversee ISO/IEC 27001 certification readiness and strengthen governance across the company's technology, documentation and operations.
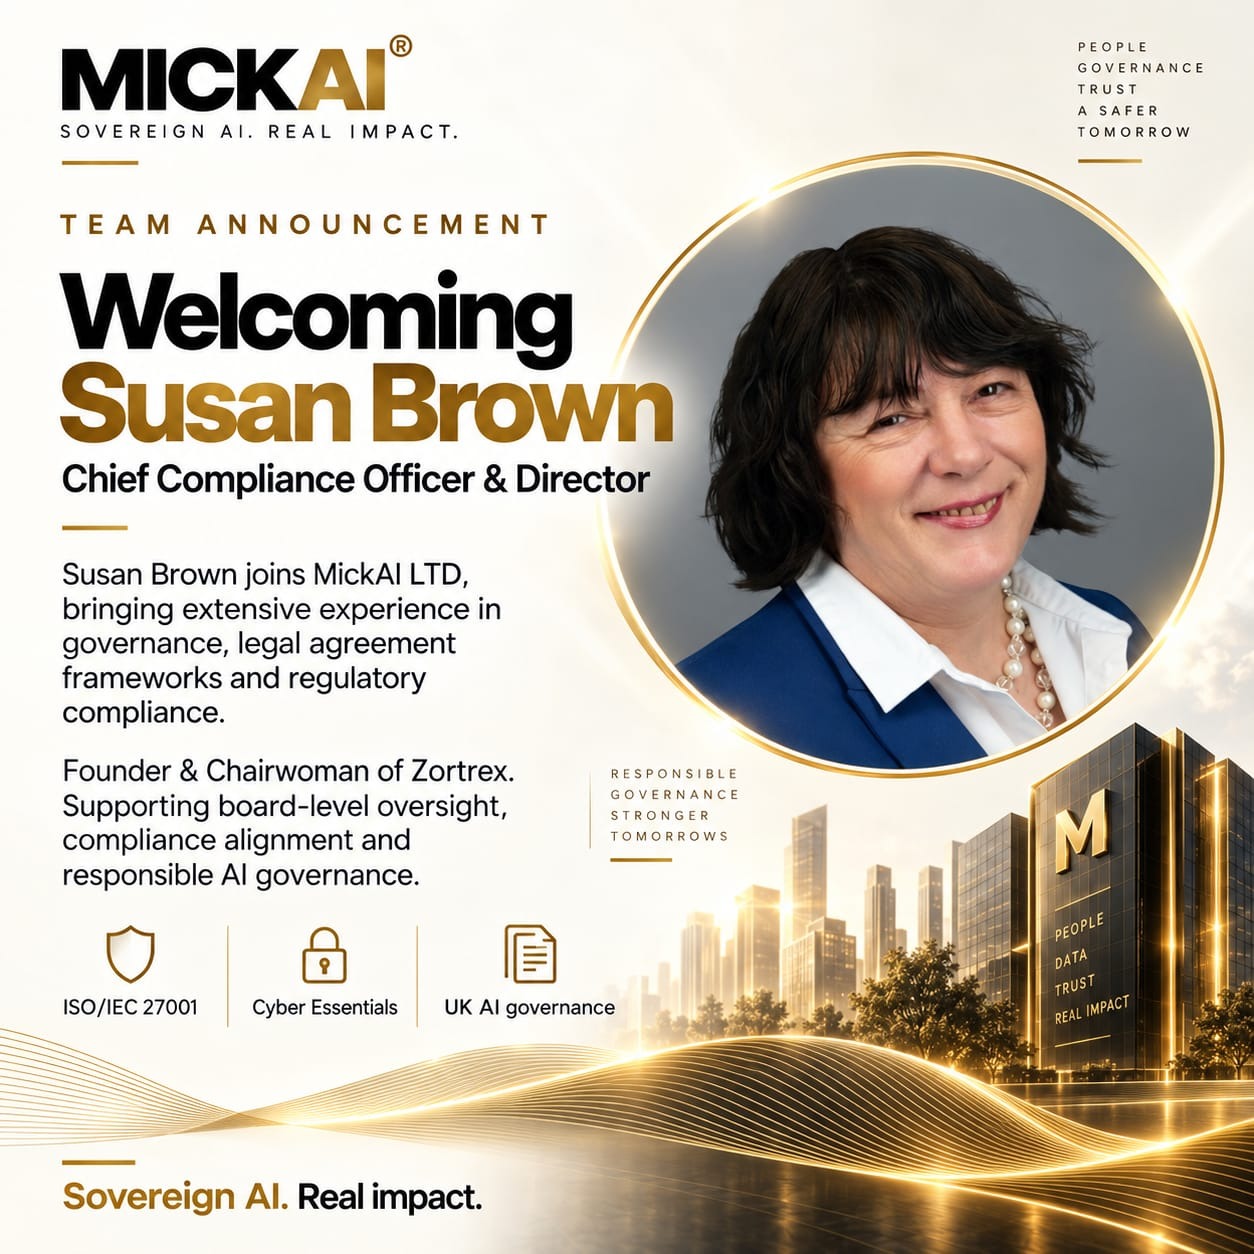
Mickai is pleased to welcome Susan Brown as Chief Compliance Officer and Director of Mickai LTD. Susan brings extensive experience in governance, legal agreement frameworks and regulatory compliance to the company's leadership team.
Susan will lead the compliance function and contribute board-level oversight as Mickai develops its Sovereign Intelligence Operating System and prepares for the next stage of delivery. Her appointment places experienced compliance leadership alongside the people designing the technology, building the business and shaping its commitments to customers.
The principle behind the appointment is straightforward: the standards expected of Mickai's technology must also be reflected in how the company operates.
Compliance across code, architecture, documents and delivery
Susan's remit will extend across the work that represents Mickai, from the code the team writes and the architectures it designs to the documents it issues, the agreements it enters into and the products it releases.
Working with the leadership and development teams, she will help translate applicable requirements into clear policies, review processes, responsibilities and evidence. This brings compliance into decisions while they are being shaped, rather than treating it as a final check before a document is sent or a product is released.
Her role will connect regulatory oversight with day-to-day practice: how risks are recorded, how information is handled, how changes are reviewed and how the company demonstrates that its commitments are being met.
Leading ISO/IEC 27001 certification readiness
A central part of Susan's role will be leading Mickai's work towards ISO/IEC 27001:2022 certification, the international standard for information security management systems. She will oversee the preparation needed to support that work, including risk assessment, documented controls, internal review, audit evidence and readiness for independent certification assessment.
She will also oversee work relating to Cyber Essentials, the UK government-backed scheme focused on technical controls against common cyber threats. This complements the wider information-security programme while remaining a separate certification scheme.
The objective is a compliance programme supported by working practices and evidence, not documentation alone. Certification milestones will be communicated separately when independently assessed and awarded.
UK and European regulatory alignment
Susan will oversee Mickai's approach to identifying, assessing and addressing the UK and European regulatory requirements relevant to its operations, products and customer engagements. This includes applicable obligations under the UK GDPR and Data Protection Act 2018, as amended by the Data (Use and Access) Act 2025, alongside EU GDPR requirements where relevant.
Her remit will also include assessing the EU AI Act requirements applicable to Mickai's role and the intended use of a system. The Act takes a risk-based approach, with obligations depending on factors including the system's purpose and whether an organisation acts as a provider or deployer.
For prospective public-sector and regulated-industry engagements, the focus will be on understanding the assurance, documentation and procurement requirements involved. It is a practical approach to regulatory alignment, not an assumption that one deployment model or certification satisfies every obligation.
Experience connecting financial governance and technology
Susan brings more than 40 years of experience in bookkeeping and accountancy, informing her approach to financial governance, record-keeping and organisational oversight.
She is the Founder and Chairwoman of Zortrex, where she leads the development of Execution Authority Control, a presence-bound execution framework for AI and autonomous systems operating in regulated finance and critical infrastructure. She is also a Director of Company Policy, providing legal agreement frameworks for small and medium-sized businesses.
Stronger governance for sovereign AI
Mickai is developing the Sovereign Intelligence Operating System to bring company knowledge, AI assistants and specialist applications together on infrastructure organisations control. Its approach centres on local operation, permission-bound work and verifiable records.
Susan's appointment strengthens the organisational oversight around that ambition. Her work will help connect technical decisions with the policies, assessments, agreements and evidence needed to support responsible delivery.
“Thank you for such a warm welcome, Micky and the whole Mickai team. Looking forward to getting stuck in. People, Data, Trust, Real Impact says it all.”
We are delighted to welcome Susan to Mickai and look forward to the experience, challenge and perspective she will bring to the team.
Frequently asked questions
What will Susan Brown do as Mickai's Chief Compliance Officer?
Susan will lead Mickai's compliance function, oversee ISO/IEC 27001 certification readiness and work relating to Cyber Essentials, and contribute board-level oversight as a director. Her remit spans applicable regulatory requirements, governance, documentation and the standards guiding Mickai's technology and operations.
Does this announcement mean Mickai is already ISO certified?
No. This is a leadership appointment and a statement of responsibility for certification readiness. Mickai does not currently hold third-party certifications. ISO/IEC 27001:2022 is the standard being referenced, not a certificate issued to Mickai.
Why does governance matter for sovereign AI?
Sovereign deployment gives an organisation greater control over where sensitive data and AI workloads run. Governance provides the policies, responsibilities, evidence and review processes needed to show that this control is being exercised responsibly.